Amazon Seller Account Hacked Recovery Playbook
You open Seller Central to check a missing disbursement and find a bank account you don’t recognize, listings you never created, and buyer messages asking about orders you can’t identify. That’s not a routine glitch. Treat it as an Amazon seller account hacked emergency until you prove otherwise. You’ve got three problems at once, an access problem, an evidence problem, and a marketplace performance problem, and fixing only the password leaves the other two untouched.
Recognize the Breach and Prioritize
A seller notices the pattern in fragments. The payout destination shows unfamiliar digits, a secondary user appears in permissions, prices drop on products the team didn’t touch, and customers complain about items that were never shipped. Any one signal could have another explanation. Several unexplained changes together justify immediate containment.
Historical reporting described attackers using stolen email-and-password credentials to alter bank-deposit information, create fake listings, and divert proceeds from both active and dormant seller accounts. That history matters because the goal is rarely just logging in. Attackers want the payout stream, a trusted storefront, or both.
Signals That Justify Immediate Action
Don’t wait for certainty if you see a cluster of these warning signs.
- Changed payout or contact details: A bank account, email, or phone number nobody on your team authorized.
- Unfamiliar users or permissions: A new secondary user, a higher-level role, or an invitation you didn’t send.
- Catalog changes you can’t explain: New listings, edited condition notes, steep discounts, or products you don’t sell.
- Order and message anomalies: Refunds, cancellations, or buyer complaints tied to orders your operation never fulfilled.
- Access alerts you didn’t trigger: Password reset notices or verification codes arriving when nobody tried to sign in.
A single listing error without access changes is probably a catalog issue. A suspension notice without unauthorized edits is an enforcement issue. But when credentials, payments, users, or listings move together, you’re looking at a suspected compromise, and you should act on that basis.
Practical rule: Contain first, document immediately after, and dispute marketplace consequences with evidence rather than memory.
Your first goals are narrow. Stop further unauthorized changes, preserve what the account shows right now, and avoid bulk edits that erase the trail you’ll need later. Don’t create a replacement seller account to work around a lockout. That adds a separate compliance risk and does nothing to recover the original account, its funds, or its history.
This article is provided for informational purposes only and is not to be construed as legal advice. No attorney-client relationship exists based on review of this article, and none of the information in this article is legal advice. Use it to organize your response and to decide when you need qualified professional help for your specific facts.
Contain Access and Payment Exposure
Work from a trusted device and a Seller Central address you type or open from a saved bookmark. Don’t use links, phone numbers, or QR codes from a suspicious message. If an unauthorized payout change or active user is visible, contain it now and capture the record right after.
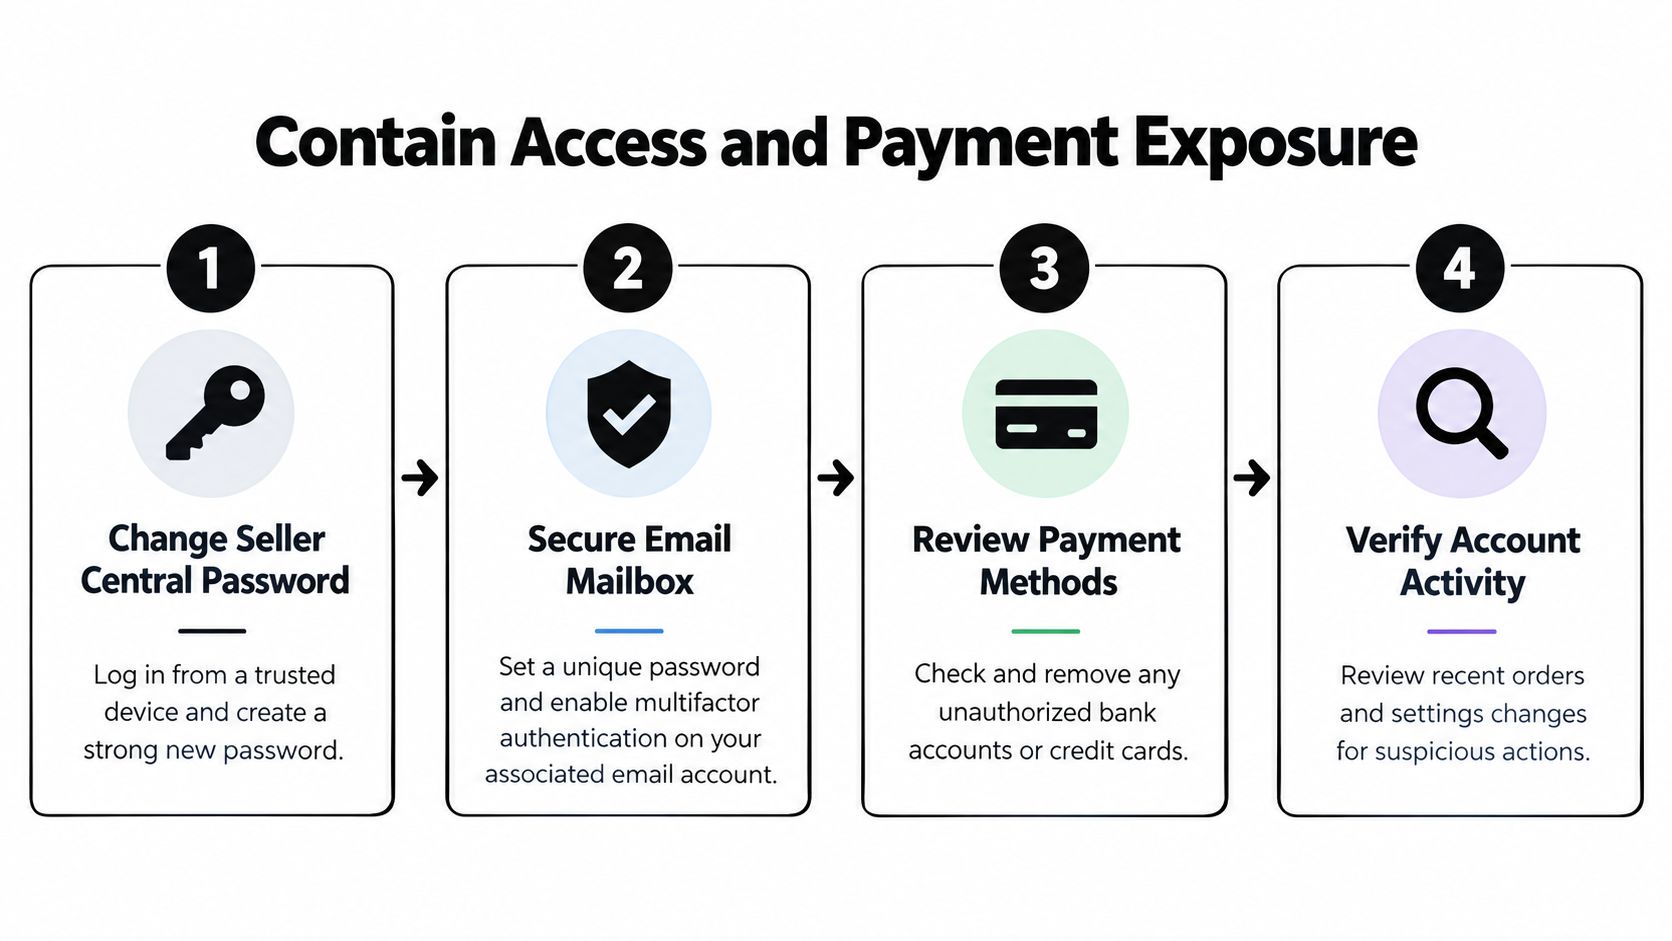
The sequence below puts the most urgent closures first.
Lock the Account and the Mailbox
- Change the Seller Central password: Create a unique password you don’t use anywhere else. If you’re locked out, use Amazon’s official account recovery or contact Selling Partner Support through a known Amazon domain.
- Secure the associated email account: Set a different unique password and enable multifactor authentication. Check recovery addresses, forwarding rules, active sessions, and connected devices, because a compromised mailbox can reset everything you just fixed.
- Review two-step verification: Confirm every method, phone number, and backup route belongs to you. Remove anything you can’t explain.
- Audit users and sessions: Delete unfamiliar secondary users, reduce excessive permissions for legitimate users during recovery, and end sessions you don’t recognize.
Amazon requires two-step verification for all Seller Central users, supporting authenticator apps, SMS, or phone calls, and cautions that email is less secure because a compromised mailbox could expose the code. Prefer an authenticator app on a device you physically control. If an attacker changed your verification method or controls your phone number, treat that channel as part of the incident, not as a safe recovery path.
Stop the Money From Moving
Check deposit methods, charge methods, disbursement status, and recent account notices as soon as access is stable. If payout details changed, call the bank or payment processor tied to the exposed route and ask what’s pending, what’s completed, and what monitoring or recall options exist. Save every alert, confirmation, and reference number you receive.
Don’t assume restoring the correct bank account reverses a transfer that already left. Amazon controls the seller account and its disbursement settings. Your financial institution controls its own payment rail. You’ll likely need both conversations, with separate case numbers, and the distinction matters if a later Amazon chargeback dispute or payment dispute follows from orders created during the takeover.
Know What Containment Doesn’t Fix
A password reset can close one door while leaving other damage in place. It doesn’t restore altered listings, release withheld funds, remove fraudulent orders, or clear account health defects. It also doesn’t prove the account is clean if a secondary user, connected app, or changed recovery setting remains.
That’s why containment ends with a check, not a celebration. Verify that only approved users remain, the verified bank account is showing, contact details match your records, and no new changes appear after the reset. Then move straight into documenting everything you found.
Build the Incident Evidence File
Your memory will blur within days. Amazon, a bank, an insurer, or law enforcement will ask what changed, when you discovered it, and what proves it. Build one chronological file that answers those questions without forcing anyone to reconstruct events from scattered emails.
Start with what’s visible in the account right now, before routine operations overwrite it.
What to Capture
- Screenshots with context: Capture full pages showing the account, the changed field, and the date. Name files so a stranger can understand them weeks later.
- Payout and order records: Download disbursement history, affected order IDs, refund records, and notices about payment changes.
- Access records: Save the user list, permission levels, login alerts, verification changes, and any invitation or removal notices.
- Catalog evidence: Record affected ASINs, listing edits, condition note changes, prices, and the approved source data they should match.
- Messages and cases: Preserve phishing emails with headers where available, buyer complaints, bank alerts, and every Amazon case communication.
A coordinated campaign compromised approximately 100 Amazon merchant accounts and altered Seller Central details so sales proceeds or loans could be routed to attacker-associated bank accounts. That scale is exactly why payout history and permission records belong in your file. They help separate an unauthorized administrative change from a legitimate business update.
Turn Files Into a Chronology
Create one log with a row for each observed change. Record the discovery time and time zone, the original value if you know it, the value you found, the correction you made, who made it, and which screenshot or download supports the row. Mark anything you don’t know as unknown instead of guessing.
Keep facts separate from interpretation. Write unauthorized modification or unknown actor unless you have proof identifying a person. That discipline protects your credibility if Amazon, a bank, or a lawyer later reviews the timeline.
The walkthrough below reinforces how to organize the record while the incident is still active.
Store a copy outside the compromised mailbox and outside any shared drive the attacker may have reached. Redact full bank numbers, tax data, authentication codes, and unnecessary customer information before sharing the file outside your organization. A concise evidence map doesn’t guarantee reinstatement, reimbursement, or a bank recall. It does make every later conversation specific, consistent, and much harder to dismiss.
Recover the Amazon Seller Account
Report the incident to Amazon as a compromise, not as a vague account problem. Words matter here. A case that says something is wrong with payments invites a generic payment answer. A case that identifies unauthorized access, lists the affected surfaces, and attaches a timeline gives the reviewer a security incident to investigate.
Use official Seller Central Help or account recovery channels reached through a known Amazon domain. Keep one primary case where possible, reference prior case numbers in updates, and assign a single internal point of contact so Amazon doesn’t receive conflicting versions from different team members.
What to Ask Amazon to Review
Amazon’s compromise-response guidance calls for changing the password from a trusted device, securing the associated email, auditing specified account areas, reporting the incident, and preserving screenshots, suspicious messages, timestamps, and case communications. Your submission should mirror that audit list and state clearly what you found in each area.
- Access and email preferences: Current sign-in status, changed email or phone settings, verification methods, and users you removed.
- Payment information: Deposit and charge methods found, the verified details you restored, and disbursements you believe were diverted or placed at risk.
- Storefront and business details: Any altered legal entity, address, tax, or contact information.
- Listings and condition notes: Affected ASINs, unauthorized offers or edits, and whether you’ve paused or corrected them.
- Orders and customer impact: Fraudulent or unfulfilled orders, refunds, cancellations, buyer messages, and related account health notices.
Close with specific requests. Ask Amazon to confirm the authorized account information, investigate the identified changes, advise on affected disbursements and orders, and tell you what verification or corrective steps remain. Vague requests produce vague replies.
Organize the Case Before You Submit
Prepare a compact packet with your store name and marketplace, masked account identifiers, the first reliable signal and its timestamp, a short chronology, containment steps already completed, and labeled evidence attachments. If you’re following a structured incident-response approach for amazon sellers from Reddog Consulting Group, use it to keep containment, documentation, and Amazon communication in the same order rather than treating each reply as a fresh start.
Record every case number, document request, response, and next checkpoint in your incident log. If Amazon separately restricts selling privileges, handle that enforcement path with the same chronology but don’t confuse the two tracks. Guidance on an account suspended by Amazon is useful when a Performance Notification requires its own response, while the security case still needs to resolve unauthorized access.
If Amazon Requests a Plan of Action
Keep it specific and short. Identify the concern Amazon raised, connect it to the documented unauthorized activity where the evidence supports that link, state the completed correction, attach proof, and describe the safeguard that prevents recurrence. Don’t claim a root cause you haven’t verified, and don’t promise outcomes you can’t control.
Your strongest submission connects each defect to a documented change and a completed fix. A general statement that you were hacked carries far less weight.
No honest adviser can guarantee reinstatement or a recovery timeline. Access status, identity verification, financial impact, and the scope of catalog or order damage all affect Amazon’s review. Track unresolved items by owner and date, keep monitoring for new changes, and don’t close the incident while an unexplained user, payout discrepancy, policy notice, or support request is still open.
Coordinate Amazon and Financial Institutions
Sellers lose time when they ask one organization to fix another organization’s problem. Amazon can review marketplace access, listings, orders, and account controls. Your bank or processor can investigate movement on its payment rail. A card issuer handles qualifying card transactions through its own dispute process. You need parallel tracks, not a single complaint forwarded everywhere.
Prepare a separate, fact-based summary for each recipient. Include transaction dates, amounts from your own records, masked account identifiers, relevant order or disbursement IDs, case numbers from the other organizations, and the exact action you’re requesting. Consistency matters, but tailoring matters too.
Who Can Address Which Loss
| Organization | Issues to Raise | Evidence to Provide |
|---|---|---|
| Amazon | Unauthorized access, users, listings, orders, disbursement settings, account health defects | Incident chronology, screenshots, affected ASINs and order IDs, containment steps, case numbers |
| Bank or payment processor | Diverted or pending transfers, exposed account details, monitoring or recall options | Bank alerts, disbursement records, dates and amounts, Amazon case number, proof of authorized account details |
| Card issuer or network | Unauthorized card charges tied to the account or connected services | Statements, transaction identifiers, dispute forms, evidence the charge wasn’t authorized |
| Law enforcement or FTC | Misuse of personal or business identifying information, broader fraud reporting | Police or FTC filings where appropriate, preserved messages, login alerts, payment change records |
FTC business data-breach guidance recommends notifying law enforcement and affected parties when appropriate and contacting the financial institution when stolen information includes credit-card or bank-account details. If employee or customer information was exposed, don’t guess about notification duties from a blog post. Get advice based on the actual data involved and the jurisdictions that may apply.
Questions That Force a Useful Handoff
Ask Amazon which disbursement records, change notices, or account reports are available to support a bank investigation. Ask the bank what written confirmation it can provide about pending, completed, returned, or unrecoverable transfers. Ask each institution what deadline applies, what form is required, and whether opening one dispute affects another remedy.
Customers need operational answers, not your full security narrative. Coordinate refunds, cancellations, and messages through Amazon’s systems and document every customer-impact decision. Avoid accusing a named person of theft without proof, and avoid telling customers a reimbursement outcome that hasn’t been confirmed.
Outcomes depend on the facts, the institutions involved, the payment method, and governing rules. One body may restore account access while another declines a transfer recall. Track each track separately in the log so a win in one place doesn’t hide an open loss somewhere else.
Explore Legal and Financial Remedies
Recovery routes aren’t interchangeable. Challenging a payment transaction, claiming marketplace losses, recovering inventory value, and pursuing an identity thief are different problems with different decision makers. Start by classifying each loss before you choose a process, because the wrong forum wastes the deadline you needed in the right one.
This article is for informational purposes only and is not to be construed as legal advice. No attorney-client relationship exists based on review of this article, and none of the information here constitutes legal advice or predicts liability, eligibility, or a favorable result. For advice on your facts, consult a qualified lawyer familiar with eCommerce disputes and the financial rules that may govern the transaction.
Match the Loss to the Route
- Diverted disbursements: Ask the receiving or sending institution, as applicable, whether a recall, return, or fraud investigation is available. Confirm deadlines in writing.
- Fraudulent card charges: Ask the issuer or processor whether a dispute or chargeback process applies to that specific transaction. Don’t assume a bank transfer carries card network rights.
- Marketplace losses: Raise refunds charged to the seller, unshipped fraudulent orders, fees, and account health defects with Amazon, tied to order IDs and your chronology.
- Inventory exposure: Document removals, stranded inventory, shipment changes, and fulfillment setting edits separately, since restoring access doesn’t value or replace stock.
- Insurance: Read the actual policy terms and notice requirements. Coverage for social engineering, funds transfer fraud, or marketplace interruption varies, and late notice can create its own problem.
Each option above requires verification. An institution may confirm that a process exists but still deny the claim on authorization, timing, documentation, or fault allocation. Preserve the denial and its stated reason, because that reason determines whether an appeal, complaint, or legal review is worth pursuing.
Identity Theft Reporting
An FTC Identity Theft Report consists of an FTC complaint or affidavit and a police report, with the FTC directing people to IdentityTheft.gov or 1-877-438-4338 and explaining that the affidavit can be taken to local police. That sequence matters when personal information was misused, accounts were opened by a thief, or collection or credit reporting problems follow.
Bring the organized file, not a pile of screenshots. A short chronology, proof of identity, records of unauthorized changes, and copies of Amazon and bank communications make the report easier to file and easier to use later.
When Legal Help Becomes Prudent
Consider qualified counsel when losses are significant, funds or inventory remain withheld, a bank or insurer denies recovery, regulated personal data may be exposed, or Amazon’s position creates a dispute you can’t resolve through support. Counsel can evaluate contracts, payment rules, insurance language, preservation duties, and litigation or demand options that a general playbook can’t decide for you.
Don’t wait until evidence is gone to have that conversation. Even before anyone discusses claims, preserve devices, messages, logs, and account exports, and stop employees from deleting suspicious emails or overwriting listing source files. Deadlines and remedies are fact specific, and delay narrows both.
Prevent the Next Seller Account Takeover
Prevention isn’t a longer password. It’s a system where one stolen credential, one former contractor, or one dormant profile can’t redirect money or publish listings under your name. Build controls around the exact surfaces attackers abused in incidents like yours, access, email, verification, users, payments, and dormant accounts.
Start with the checklist you can complete immediately after recovery stabilizes.
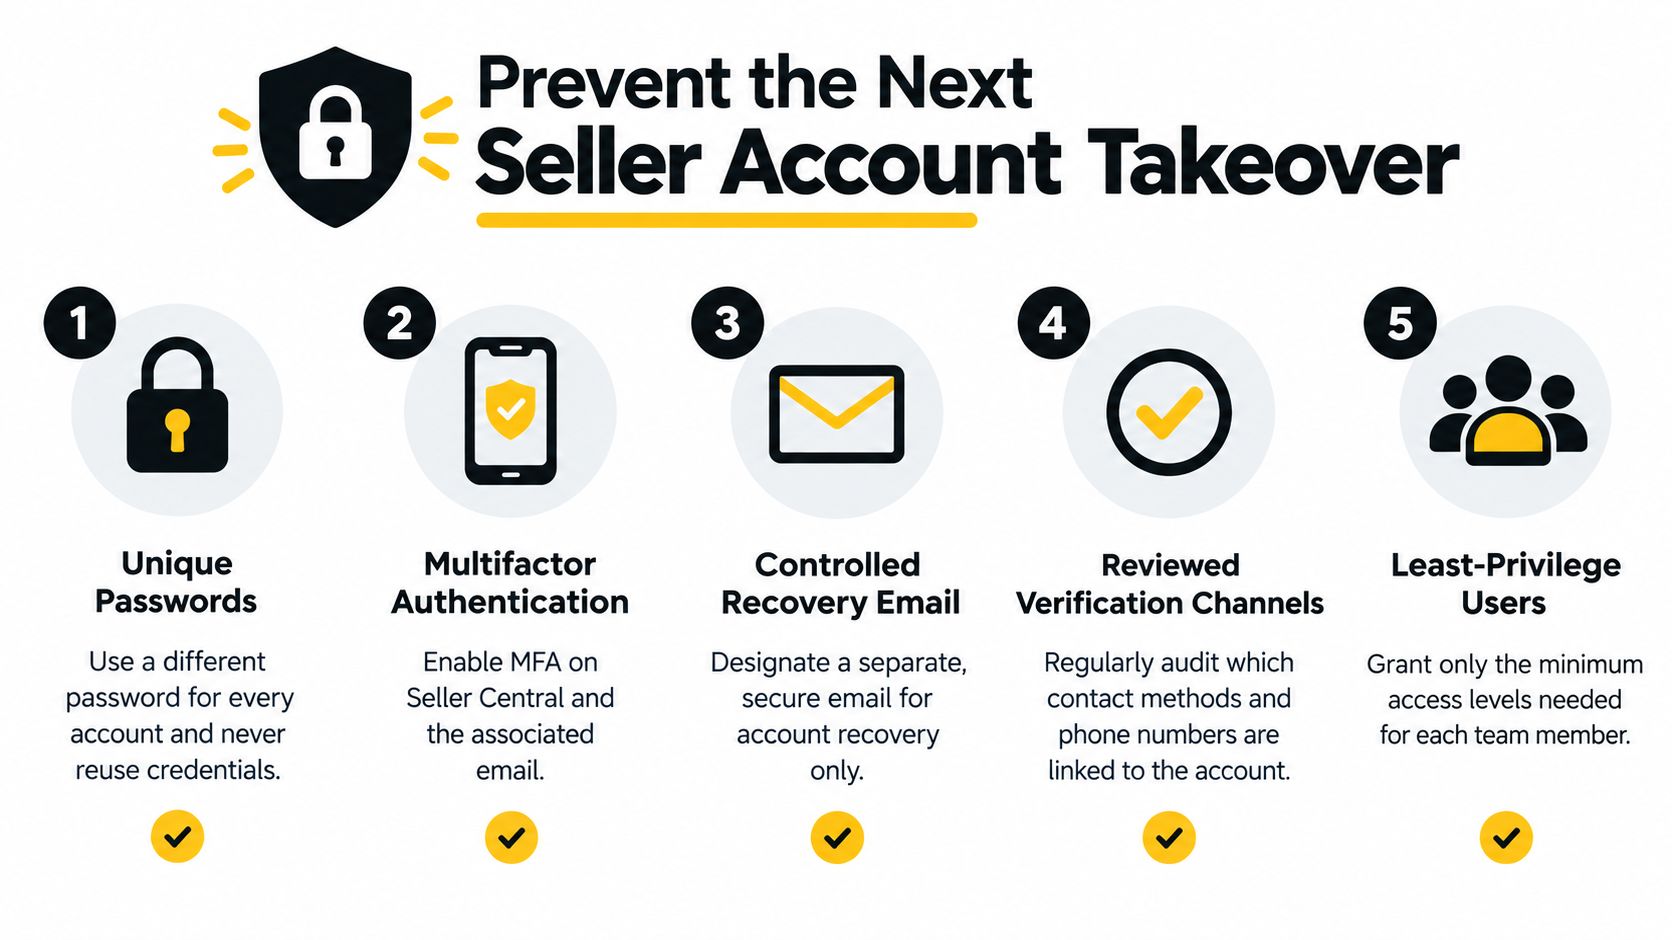
Access Controls That Hold Up
- Unique passwords everywhere: Use a password manager and never reuse the Seller Central password for email, banking, advertising, or supplier portals.
- Multifactor authentication on both doors: Protect Seller Central and the associated mailbox. Securing one while leaving the other open is the most common false finish.
- Controlled recovery email: Limit who can access it, review forwarding rules and recovery contacts, and treat it as a security asset rather than a shared inbox.
- Least-privilege users: Give employees and agencies only the permissions their work requires. Remove access the same day a person or vendor relationship ends.
- Connected apps and brand roles: Review authorized applications, API connections, and Brand Registry roles regularly. Sellers strengthening brand controls can compare these access checks with the broader protections covered in Amazon Brand Registry guidance on newer brand protection tools.
Payment Change Discipline
Create a rule that nobody changes a payout destination based on an email, chat message, or Seller Central prompt alone. Verify material payment changes through a known, separate contact method, require dual approval from two authorized people, and record the approval in your finance log. If the business is too small for two approvers, require a waiting period and a call to a prewritten internal number before the change takes effect.
Any payout change nobody can trace to two known people and a written approval should be treated as unauthorized until proven otherwise.
Reconcile disbursements against orders and bank deposits on a regular schedule. A missing payout discovered during reconciliation is a finance alert, not something to watch for another cycle. Keep bank alerts routed to a monitored address that survives staff absence.
Dormant Accounts and Rehearsed Response
Inactive seller profiles still carry a storefront, credentials, and marketplace trust. Secure dormant accounts with the same passwords, verification, mailbox protection, and periodic login checks as active ones, or close them properly if the business no longer needs them. An account nobody watches is the easiest one to abuse without detection.
Maintain an incident folder before you need it. Include contact lists for the account administrator, finance lead, bank, insurer, IT support, and counsel, plus templates for the chronology, evidence log, Amazon case summary, and bank notification. Rehearse who can change passwords after hours, who calls the bank, and who owns customer operations.
After recovery, monitor login alerts, payout changes, user access, listings, orders, connected apps, and open Amazon cases until every unexplained item has an owner and a resolution. Credential changes alone aren’t a complete defense. Durable protection comes from controlled access, verified payment changes, watched dormant accounts, and a team that already knows its first moves.
If your seller funds, inventory, or account access remain at risk after a takeover, LA Law Group, APLC helps California businesses and Amazon sellers assess reinstatement, payment disputes, and related eCommerce claims with direct attorney involvement. Visit LA Law Group, APLC to request a prompt case assessment and discuss the documented facts of your incident.
Attorney Advertising. This article is general information, not legal advice, and does not create an attorney-client relationship. Prior results do not guarantee a similar outcome.